

I will be installing on Debian Lenny, but there is no difference with Debian Squeeze.
SAMS It is a system for managing user access through a proxy server to Internet resources. It is ideal for use in both private companies and government agencies. All the work on proxing, redirecting requests, caching and authorization is taken over by the proxy server Squid, and SAMS deals with traffic accounting and user management.
Squid A software package that implements the function of a caching proxy server for HTTP, FTP, Gopher and (if appropriate) HTTPS protocols. Developed by the community as an open source program (distributed under the GNU GPL).
Start installing and configuring our software package.
Installation and configuration of squid
To begin with, add a repository to source.list from which we will install all programs:
For Debian Lenny:
vi /etc/apt/sources.list
deb http://archive.debian.org/debian/ lenny main contrib non-free
For Debian Squeeze:
vi /etc/apt/sources.list
deb http://mirror.yandex.ru/debian squeeze main contrib non-free
Updating the repository
aptitude update
Update all available packages
aptitude dist-upgrade
Install a proxy server Squid
aptitude install squid
Install the file manager mc
aptitude install mc
Installation of the text editor vim
aptitude install vim
Install web server Apache2, MYSQL, PHP5, phpmyadmin
aptitude install apache2 mysql-server php5 phpmyadmin
After successfully installing squid, proceed to its setting:
Copy the configuration file into an archive
cp /etc/squid/squid.conf /etc/squid/squid.conf_backup
We open the configuration file squid.conf convenient for you editor
vi It requires reading the user’s instructions. In order to complete the express course, launch a team vimtutor and pass the main commands to use the program.
mcedit - easier to work for a beginner linuxoid
For simplicity of description, I will describe the work with the editor. MC
mcedit /etc/squid/squid.conf
press F7A search box will appear, enter into it what you need to find by clicking Enter
If we find the wrong thing, repeat the search again, and so on until we find the right line. After you have made the necessary changes and want to save the file click F2 And we accept the change. After saving to close the saved file, click F10
Next, I’ll write what we’re looking for and how it should look after the change (the first one looks like it should, the others are like this):
was:
#  TAG: visible_hostname
#       If you want to present a special hostname in error messages, etc,
#       define this.  Otherwise, the return value of gethostname()
#       will be used. If you have multiple caches in a cluster and
#       get errors about IP-forwarding you must set them to have individual
#       names with this setting.
#
#Default:
# none
became:
#  TAG: visible_hostname
#       If you want to present a special hostname in error messages, etc,
#       define this.  Otherwise, the return value of gethostname()
#       will be used. If you have multiple caches in a cluster and
#       get errors about IP-forwarding you must set them to have individual
#       names with this setting.
#
#Default:
visible_hostname inetservname
was:
http_port 3128
became:
http_port 3128 transparent
Attention!! If your users are logged in using a password, transparent authorization will not work, you need to prescribe IP:PORT of your proxy server in the user's browser.
was:
# icp_port 3130
became:
icp_port 0
was:
# cache_mem 8 MB
became:
cache_mem 256 MB
was:
# maximum_object_size_in_memory 8 KB
became:
maximum_object_size_in_memory 512 KB
was:
# maximum_object_size 20480 KB
became:
maximum_object_size 120480 KB
was:
# cache_dir ufs /var/spool/squid 100 16 256
became:
cache_dir ufs /var/spool/squid 5000 32 256
was:
# cache_swap_low 90
# cache_swap_high 95
became:
cache_swap_low 90
cache_swap_high 95
was:
# logfile_rotate 0
became:
logfile_rotate 5
was:
acl SSL_ports port 443          # https
acl SSL_ports port 563          # snews
acl SSL_ports port 873          # rsync
acl Safe_ports port 80          # http
acl Safe_ports port 21          # ftp
acl Safe_ports port 443         # https
acl Safe_ports port 70          # gopher
acl Safe_ports port 210         # wais
acl Safe_ports port 1025-65535  # unregistered ports
acl Safe_ports port 280         # http-mgmt
acl Safe_ports port 488         # gss-http
acl Safe_ports port 591         # filemaker
acl Safe_ports port 777         # multiling http
acl Safe_ports port 631         # cups
acl Safe_ports port 873         # rsync
acl Safe_ports port 901         # SWAT
became:
acl SSL_ports port 443          # https
#acl SSL_ports port 563          # snews
#acl SSL_ports port 873          # rsync
acl Safe_ports port 80          # http
acl Safe_ports port 21          # ftp
acl Safe_ports port 443         # https
#acl Safe_ports port 70          # gopher
#acl Safe_ports port 210         # wais
#acl Safe_ports port 1025-65535  # unregistered ports
#acl Safe_ports port 280         # http-mgmt
#acl Safe_ports port 488         # gss-http
#acl Safe_ports port 591         # filemaker
#acl Safe_ports port 777         # multiling http
#acl Safe_ports port 631         # cups
#acl Safe_ports port 873         # rsync
#acl Safe_ports port 901         # SWAT
was:
#  TAG: url_rewrite_program
#       Specify the location of the executable for the URL rewriter.
#       Since they can perform almost any function there isn't one included.
...
#Default:
# none
became:
#  TAG: url_rewrite_program
#       Specify the location of the executable for the URL rewriter.
#       Since they can perform almost any function there isn't one included.
...
#Default:
url_rewrite_program /usr/bin/samsredir
was:
#Default:
# url_rewrite_children 5
became:
url_rewrite_children 5
was:
#auth_param basic program <uncomment and complete this line>
#auth_param basic children 5
#auth_param basic realm Squid proxy-caching web server
#auth_param basic credentialsttl 2 hours
became:
auth_param basic program /usr/lib/squid/ncsa_auth /etc/squid/ncsa.sams
auth_param basic children 5
auth_param basic realm Squid proxy-caching web server
auth_param basic credentialsttl 2 hours
! If you are using an internal DNS server inside the network, you can tell the Squid proxy to use it by writing:
In order to use your local DNS server, we change:
was:
#  TAG: dns_nameservers
...
#Default:
# none
became:
#  TAG: dns_nameservers
...
#Default:
dns_nameservers 192.168.1.1
Save the changes and proceed to install SAMS.
Installation of SAMS 1.5
The necessary dependencies must be established:
apt-get install apache2 php5 mysql-server mysql-client build-essential autoconf automake libtool g++ php5-gd libmysqlclient15-dev php-fpdf
When asked to enter the root mysql password, enter and repeat, as well as write on a piece of paper or in a notebook, so as not to forget.
We make a backup of configs that we will change:
cp /etc/squid/squid.conf /etc/squid/squid.conf_backup
cp /etc/apache2/apache2.conf /etc/apache2/apache2.conf_backup
cp /etc/php5/apache2/php.ini /etc/php5/apache2/php.ini_backup
Configuring PHP
SAMS can work with PHP in safe_mode=On mode. But this requires additional configuration settings. To do this, we edit the php configuration file. /etc/php5/apache2/php.ini.
1. Turn on the safe mode (this is optional, for example, I do not turn on). This is why we set the safe_mode setting.
safe_mode = On
!! Attention.If you have an improt in rejik ban sheets gives an error in the web interface: can't open sams config file data/urlist.txt
Safe_mode should be placed in Off, which means:
safe_mode = Off
2. SAMS uses system commands for some functions of the interface, such as wbinfo. In safe_mode mode, php blocks access to system commands. Php allows you to execute system commands located in a directory specified by the safe_mode_exec_dir parameter. Modify this parameter:
safe_mode_exec_dir = "/usr/share/sams/bin"
3. Next, we allow the execution of system scripts from php code. We search for a configuration file and remove the ban on calling phpinfo system shell_exec exec functions from it:
disable_functions = "chdir,dl,ini_get_all,popen,proc_open,passthru,pcntl_exec"
4. In order to be able to fill in large ban lists in PHP, we increase the maximum query size and file size.
Max. size
became:
; Maximum size of POST data that PHP will accept
post_max_size = 50M
Max. file size
became:
; Maximum allowed size for uploaded files.
upload_max_filesize = 50M
4. All. PHP is ready to go.
You need to restart the web server to reread the settings from php.ini:
/etc/init.d/apache2 restart
Installable SAMS:
Go to the directory where we will download installation packages, create a folder samsWe go to it and we pump the installation packages:
cd /usr/src/
mkdir sams
cd sams
We download Samsung packages for our architecture:
For amd64:
wget http://nixdev.net/release/sams/debian/lenny/sams_1.0.5_amd64.deb
wget http://nixdev.net/release/sams/debian/lenny/sams-web_1.0.5_all.deb
wget http://nixdev.net/release/sams/debian/lenny/sams-doc_1.0.5_all.deb
For the i386:
wget http://nixdev.net/release/sams/debian/lenny/sams_1.0.5_i386.deb
wget http://nixdev.net/release/sams/debian/lenny/sams-web_1.0.5_all.deb
wget http://nixdev.net/release/sams/debian/lenny/sams-doc_1.0.5_all.deb
Install the downloaded packages:
dpkg -i *.deb
A pseudographic window will appear:
Настраивается пакет sams

SAMS require additional manual configuration

Currently SAMS package not ready to work out of box. Starting of samsdaemon disabled in init.d script.

Please read /usr/share/doc/sams/README.Debain for description of additional configure step.

                                    <Ok>
Press OK.
Include Sams in the file by correcting /etc/init.d/sams
was:
SAMS_ENABLE=false
became:
SAMS_ENABLE=true
Adjust the configuration file to the address /etc/sams.conf
Correct:
MYSQLPASSWORD=yourpassword
REJIKPATH=/usr/local/rejik3
Next, check whether squid is running and if the command outputs a number then it is running, and then we stop the proxy server.
pidof squid
8534
/etc/init.d/squid stop
* Stopping Squid HTTP proxy squid                                    [ OK ]
Now we will recreate the proxy server cache with the command:
squid -z
2009/02/16 15:55:20| Creating Swap Directories
At this stage, the squid setup is finished, now we run a proxy server with the command:
init.d/squid start
We are preparing mysql base for the work of Sams:
go under the root user and password that we wrote in advance in a notebook to our server at:
http://ip_server/phpmyadmin
Then we press the button.SQL And you put the code in the window. Perform SQL query(s) on the localhost server necessarily change the password yourpassword on:
GRANT ALL ON squidctrl.* TO sams@localhost IDENTIFIED BY "yourpassword";
GRANT ALL ON squidlog.* TO sams@localhost IDENTIFIED BY "yourpassword";
You need to press. OK:
Be sure to fill the databases created for Samsung with commands in the server console:
mysql -u sams -pyourpassword < /usr/share/sams/mysql/sams_db.sql
mysql -u sams -pyourpassword < /usr/share/sams/mysql/squid_db.sql
Copy - paste and execute by changing yourpassword password to your own:
! Attention!!!
If you are configuring Debian Squeeze, you need to add a repository from Debian Lenny in order to establish the necessary dependencies.
Add a repository that has already been archived in a file /etc/apt/sources.list team:
echo "deb http://archive.debian.org/debian/ lenny main contrib non-free" >> /etc/apt/sources.list
Update the repository with a team:
aptitude update
We establish the necessary dependence by the team:
aptitude install libmysqlclient15off
In order to enter the SAMS control panel, you need to enter the address in the browser http://ip_server/samswhere ip_server is the IP address of the server to which we installed.
Administrator entrance:
Login: admin
Password: qwerty
Entrance under the auditor:
Login: auditor
Password: audit
I strongly advise you to change the password immediately, and write it down in a notebook.
If you install SAMS on a server already working with any hosting control panel, such as ISPmanager, create for example a user samsweb with the domain sams.site.loc and give him permission to CGI, as well as configure the domain to work through php CGI, and in the domain folder simply mount the contents of the folder sams command:
mount --bind /usr/share/sams /var/www/samsweb/data/www/sams.site.loc/
Run this command and then put it in a file. /etc/rc.localThen, when loading the server, the folder is mounted automatically.
You also need to give rights to the contents of the folder for your user by command:
chown -R samsweb:samsweb /var/www/samsweb/data/www/sams.site.loc/
It should be something like this:
....
# bits.
#
# By default this script does nothing.

mount --bind /usr/share/sams /var/www/samsweb/data/www/sams.site.loc/
.....
If the installation has made such an error:
Fatal error: Cannot redeclare GetHostName() in /var/www/samsweb/data/www/sams.site.loc/src/configtray.php on line 20
It is necessary to enter into the scripts of SAMS:
cd /usr/share/sams/
vi src/webconfigtray.php
was:
function GetHostName()
{
  if(!($value=getenv('SERVER_NAME')))
     {  $value="N.A."; }
  return($value);
}
became:
//function GetHostName()
//{
//  if(!($value=getenv('SERVER_NAME')))
//     {  $value="N.A."; }
//  return($value);
//}
vi src/configtray.php
was:
function GetHostName()
{
  if(!($value=getenv('SERVER_NAME')))
     {  $value="N.A."; }
  return($value);
}
became:
//function GetHostName()
//{
//  if(!($value=getenv('SERVER_NAME')))
//     {  $value="N.A."; }
//  return($value);
//}
After that, the web interface will open normally.
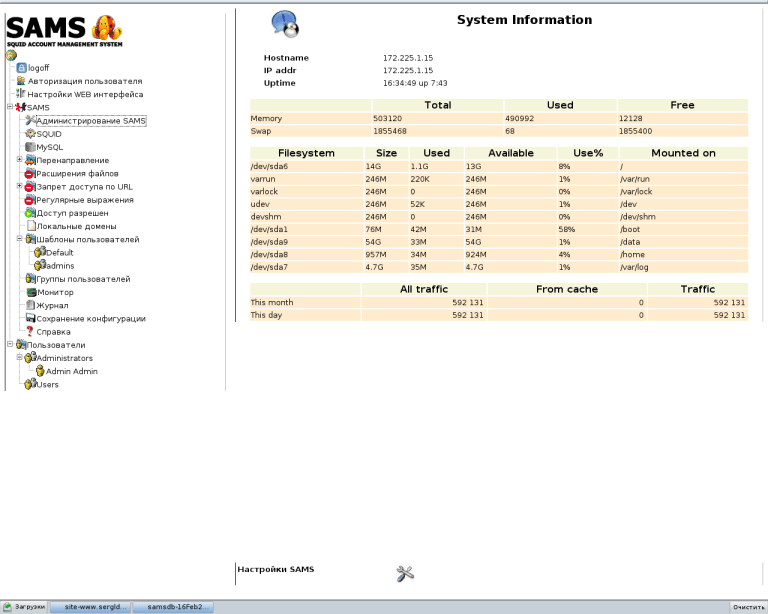
Screenshots of setting up SAMS through the web interface:
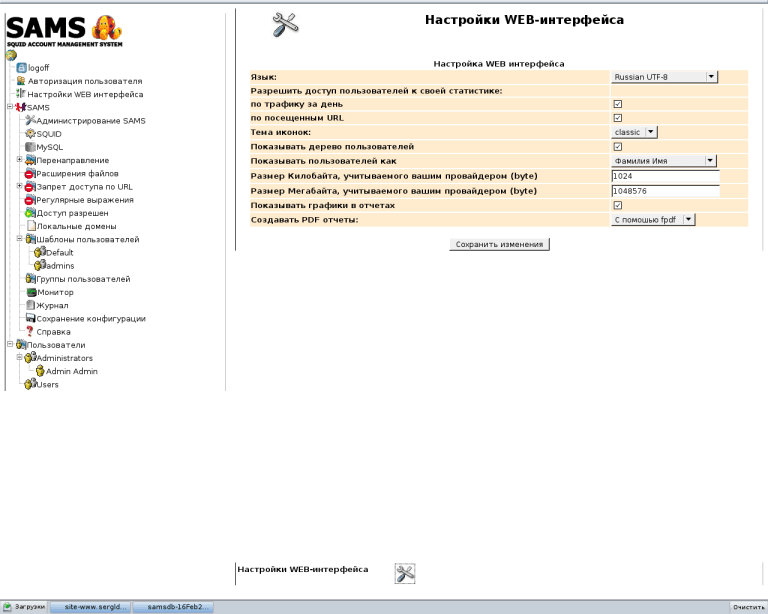
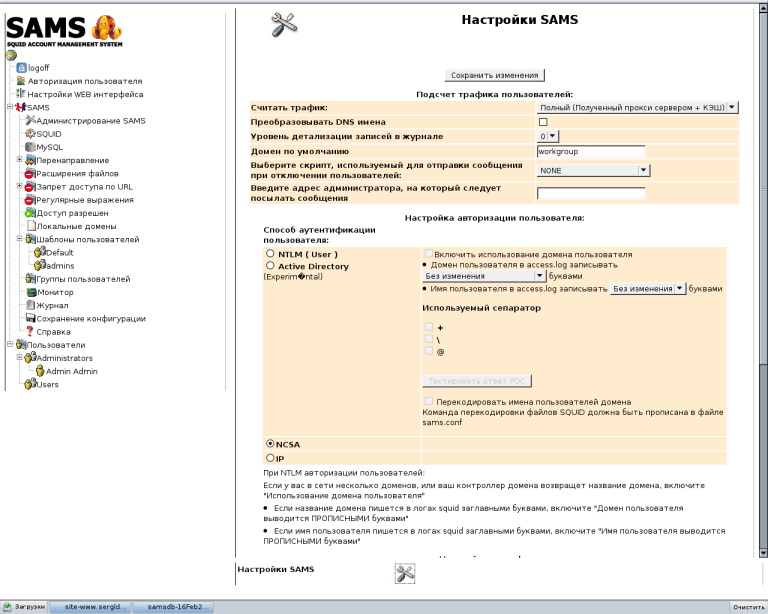
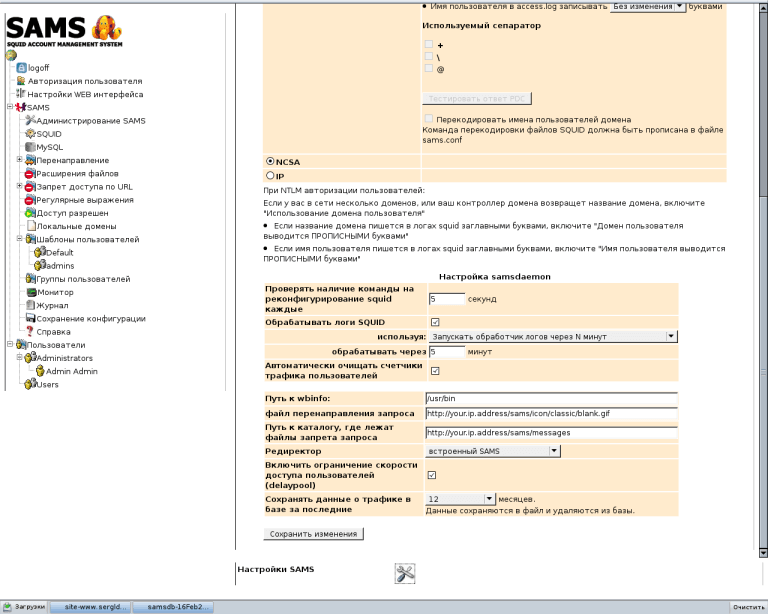
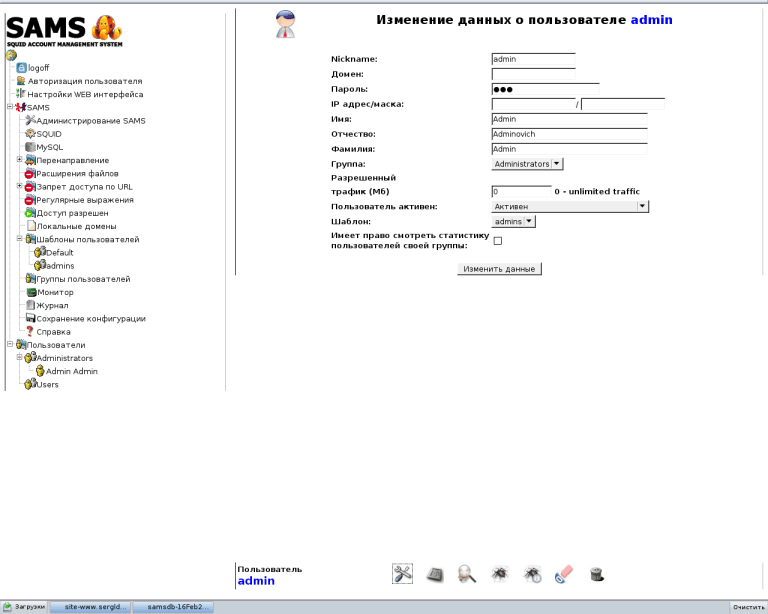
Attention!!!
For users subject to restrictions, the standard message that displays Samsung looks like this:
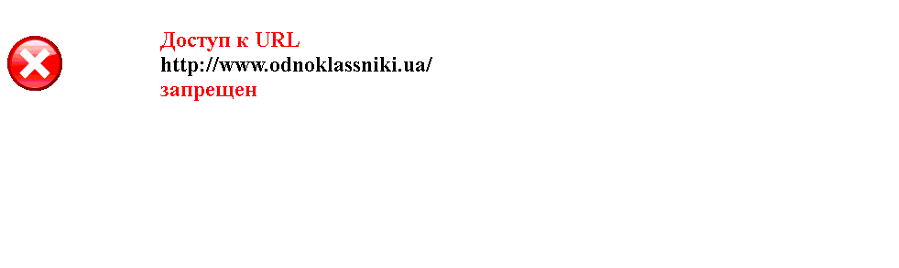
In order for the user to display his file written in HTML, you need to create the file itself which will be displayed to the user by the command that is limited:
touch /usr/share/sams/messages/file_denied.html
file
mcedit /usr/share/sams/messages/blocked.php
Need to change
was:
if($action=="rejikdenied"||$action=="sgdenied")
    {
       print("  <TR><TD><IMG SRC=\"$path$ICONSET/denied.gif\">");
       print("  <TD> ");
       print("<P><FONT COLOR=\"RED\"><B><H2>$blocked_php_3 <BR></FONT>");
       print("$url<BR> <FONT COLOR=\"RED\">$blocked_php_4</H2></B></FONT> ");

       exit(0);
    }
became:
  if($action=="rejikdenied"||$action=="sgdenied")
    {
//       print("  <TR><TD><IMG SRC=\"$path$ICONSET/denied.gif\">");
//       print("  <TD> ");
//       print("<P><FONT COLOR=\"RED\"><B><H2>$blocked_php_3 <BR></FONT>");
//       print("$url<BR> <FONT COLOR=\"RED\">$blocked_php_4</H2></B></FONT> ");
       print(file_get_contents('file_denied.html'));
       exit(0);
    }
After that, the user who has fallen under the restriction will be displayed prepared by you HTML file located on the way. /usr/share/sams/messages/file_denied.html
My example is a simple file:
<!DOCTYPE html PUBLIC "-//W3C//DTD HTML 4.01 Transitional//EN">
<html>
<head>
<title>Site Blocked</title>
<meta http-equiv="Content-Type" content="text/html; charset=utf8">
</head>
<body bgcolor="#000000" text="#c8c8c8" link="#c8c8c8">
<table align="center" border="0" width="640">
<tr><td align="center">

<h1>Содержимое данного сайта заблокировано для просмотра в сети "Ваша фирма".</h1>
<h2  align="justify"><font color="red">Этот сайт внесен в список запрещенных адресов как мешающие полноценной работе.</font>
<br>Просим извинить за неудобства. Если этот сайт Вам настоятельно требуется для работы, будте добры сообщить администратору сервера об этом.
</h2>

<hr>
</table>
</body>
</html>
Attention!!!
In the settings sams into Method of authenticating the user Choose the IP or NCSA method you need and make sure to User Templates - DefaultSame way. Next, you create the necessary templates and one of these templates you can attach to any user.
Each template can be linked to restrictions on where you can go and where not, as well as the amount of traffic available to the user, channel speed for the entire template and channel speed for the individual user.
Continuation of the instructions is at the address:
In this instruction, we install the redirector program. Rejik And we configure it through the web interface. SAMS
And in this instruction, we install and configure the online proxy server statistics program. Sqstat

comment